












Monitoring & optimisation
Managed Microsoft monitoring and optimisation services
See issues early, resolve them faster and optimise continuously. 24/7 managed monitoring across Azure, Microsoft 365 and business applications: our UK-based Microsoft specialists monitor, investigate and respond to issues, then use what we learn to improve performance, resilience and cost.
What's covered
Proactive cloud monitoring across your Microsoft environment
One managed service providing visibility across the platforms your organisation depends on. We combine Microsoft-native monitoring, observability and engineering expertise to detect issues early, turn alerts into action and use every incident to improve the environment over time.
Azure infrastructure monitoring
Compute, storage, networking and platform services continuously monitored for availability, capacity, health and performance.
Microsoft 365 service health
Service incidents, advisories, Message Center changes and platform health reviewed so issues are identified and communicated quickly.
Application performance & observability
Application health, errors, response times, dependencies and user journeys monitored across your business-critical services.
Network & connectivity
VPN, ExpressRoute, gateways, DNS, certificates and network paths monitored so connectivity issues are caught early.
Security & identity signals
Entra ID, Defender and identity signals triaged, with potential security incidents escalated through agreed security processes.
Backup, data & scheduled jobs
Backups, pipelines, integrations, refreshes and scheduled jobs monitored so failures do not remain hidden.
Performance & resilience
Trends, bottlenecks, capacity and resilience risks analysed before they develop into user-impacting problems.
Cost & licence optimisation
Idle capacity, oversized resources, telemetry costs and unused licences identified so spend better reflects actual demand.
More than alerting
Alerts that lead to action, not noise
Monitoring only creates value when somebody acts on what it finds. Our engineers investigate alerts, identify recurring causes and continuously tune your environment so reliability improves over time.
Alert tuning
Thresholds, suppression and alert rules tuned around your services to reduce noise and highlight what genuinely needs attention.
Alert triage & response
Alerts are assessed, prioritised and acted on by engineers rather than simply forwarded to your internal team.
Root-cause analysis
Recurring faults are investigated across infrastructure, applications, dependencies and configuration so the underlying cause can be addressed.
Automated remediation
Where appropriate, approved alerts can trigger automated workflows or remediation actions for known and repeatable issues.
Trend & service health analysis
Performance, availability and capacity trends are reviewed across complete business services, not just individual resources.
Service reporting & improvement
Regular service reporting highlights availability, incidents, trends, recurring issues and prioritised improvements.
Continuous optimisation
Cloud performance, resilience & cost optimisation
Monitoring gives us the evidence to improve your environment. We use operational data to identify bottlenecks, resilience risks, unnecessary cost and monitoring gaps, then prioritise improvements with your team.
Performance optimisation
Identify application, database, compute and network bottlenecks and tune services using real operational telemetry.
Resilience optimisation
Identify single points of failure, capacity constraints and availability risks and prioritise improvements.
Cost optimisation
Rightsize resources, identify waste and optimise reservations, savings plans, licences and monitoring-related costs.
Monitoring optimisation
Continually refine alerts, dashboards, telemetry collection, retention and escalation routes as the environment evolves.
Powered by Konsolute Technology
Proprietary tools that extend Microsoft-native monitoring
Alongside Microsoft-native monitoring and security services, Konsolute has developed its own technology to give our engineers deeper operational visibility across your environment.
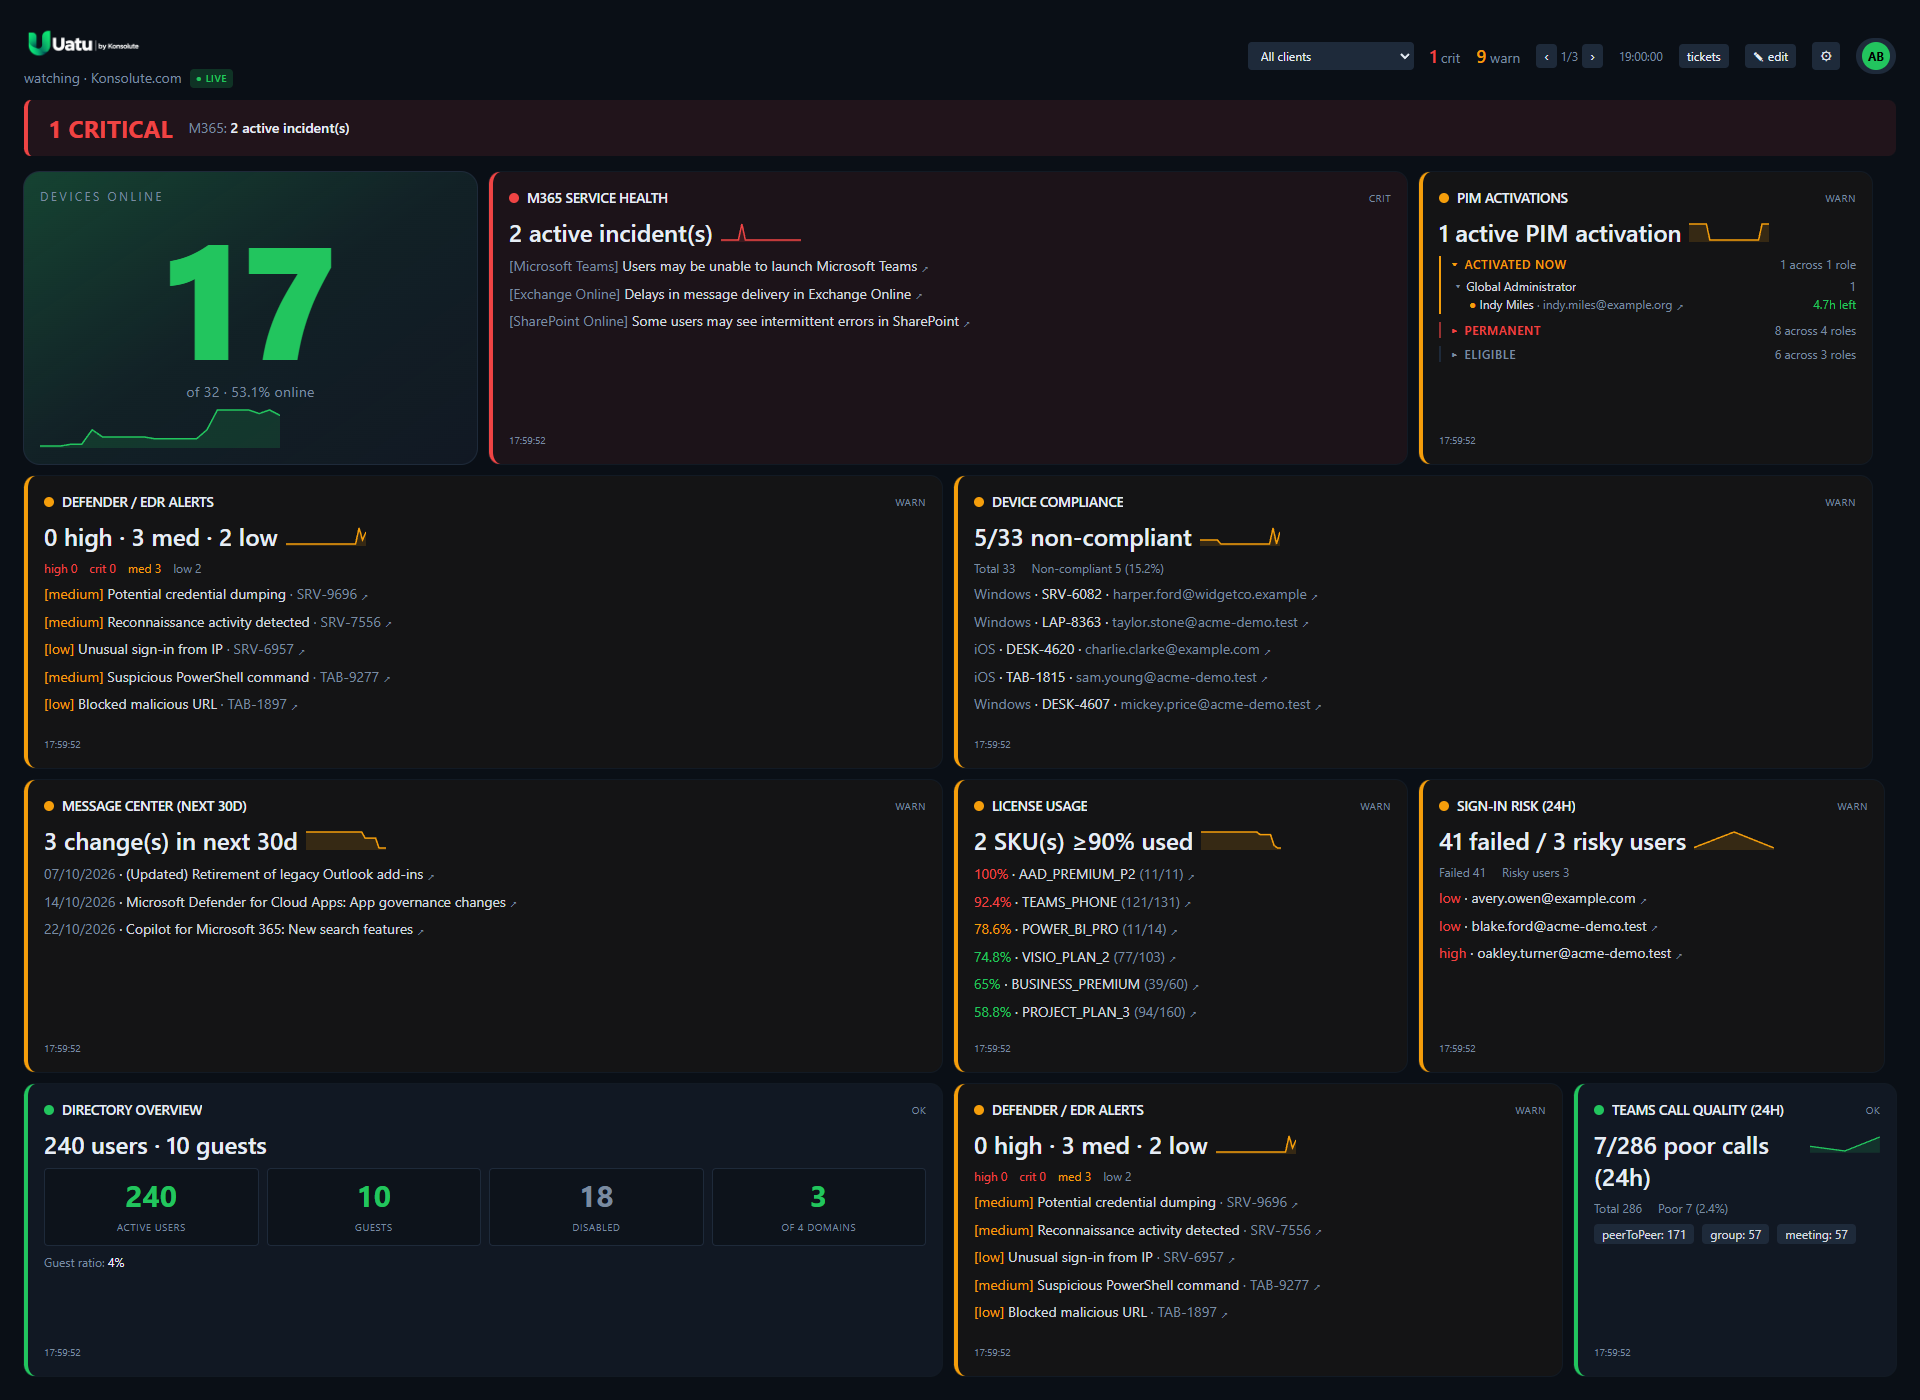
Uata: proactive monitoring dashboard
Uata is Konsolute's proactive monitoring dashboard, giving near real-time visibility of platform health across your Microsoft environment. It brings key operational signals into a single view, so engineers can spot degradation, service issues and emerging trends without waiting for users to report problems.
Continuous visibility
Uata gives our engineers proactive visibility across the Microsoft services and operational signals that matter to your organisation.
Emerging risk detection
Identify service degradation, configuration risks and recurring faults before they develop into larger operational incidents.
Connected insight
Operational signals are reviewed alongside Azure Monitor, Microsoft 365, Application Insights and other telemetry to build a clearer view of service health.
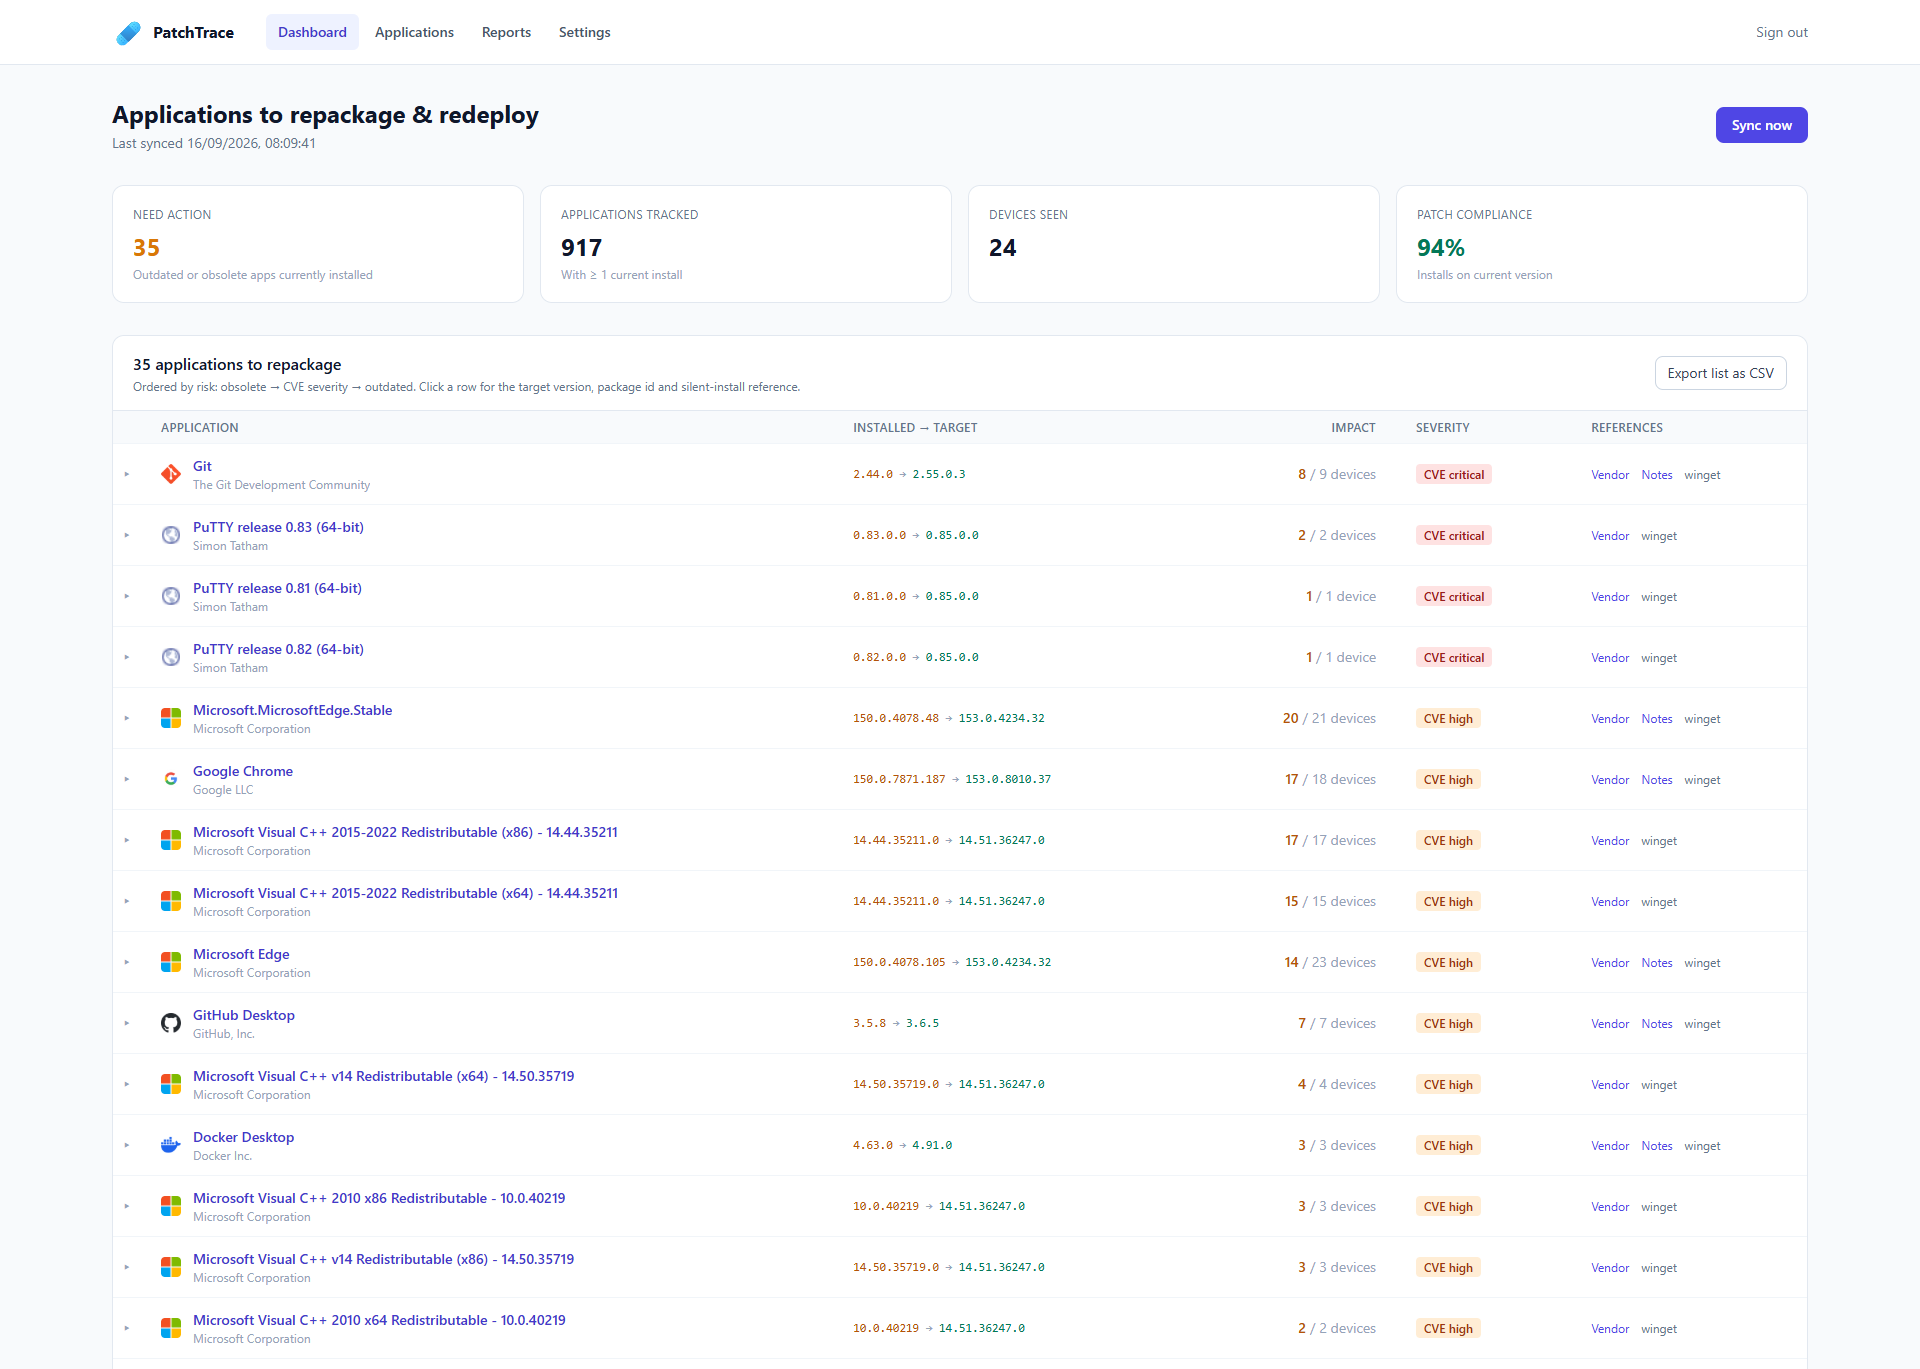
PatchTrace: application vulnerability and patch intelligence
PatchTrace correlates application information with vulnerability intelligence, including CVE and NIST data, giving greater visibility of applications that may expose the organisation to security or operational risk.
Application inventory & lifecycle visibility
Build a clearer view of the applications installed across your environment, including version, age, patch status and whether software is becoming obsolete or unsupported.
Vulnerability identification & risk prioritisation
Identify applications associated with known vulnerabilities using CVE and NIST-informed data, helping teams understand where genuine software risk exists and which issues should be addressed first.
Remediation & patch prioritisation
Turn application and vulnerability data into an actionable remediation view, highlighting which applications need patching, upgrading, replacing or removing to reduce operational and security exposure.
Platforms and activities
Managed Azure, Microsoft 365 & application monitoring
Your managed service can cover any combination of these platforms and activities. The final scope is designed around your environment, critical services, hours of cover and the responsibilities retained by your internal team.
Azure Monitor, Log Analytics & service health
End-to-end visibility across the Azure services your workloads depend on.
Network & connectivity monitoring
Identify connectivity problems before users report them.
Microsoft 365 service health
Understand whether an issue is within your environment or Microsoft's platform.
Identity & security signals
Spot identity-related operational and security issues early.
Application performance & observability
Understand application health from infrastructure through to the user's experience.
Data, backup & job monitoring
Know when critical processing, integration and recovery jobs fail.
Performance & resilience optimisation
Use operational telemetry to make critical services faster, healthier and more resilient.
Cost, licence & telemetry optimisation
Reduce unnecessary cloud and monitoring spend while retaining the visibility your teams need.
Regulated environments
Monitoring for government, nuclear & regulated organisations
Monitoring a sensitive environment means treating logs, telemetry, privileged access and incident information with the same care as the systems themselves. Access requirements and engineer clearance (SC or DV) are agreed before the service begins.
SC and DV-cleared engineers
SC and DV-cleared engineers are available for environments that require additional personnel assurance and access controls.
Controlled access to telemetry
Least-privilege, read-first access to monitoring data and systems, with administrative access introduced only where agreed and required to implement a fix.
UK-based monitoring
Alerts are reviewed and acted on by UK-based Microsoft engineers, while Microsoft-native monitoring data can remain within your own tenant and subscriptions.
Evidence for assurance
Monitoring history, availability information, incident records and response evidence can support internal assurance, audit and regulatory reporting requirements.
Managed or co-managed
Monitoring that fits your IT team
Hand monitoring and response to Konsolute, or retain operational ownership and use our Microsoft specialists for out-of-hours cover, complex incidents, alert tuning and optimisation. We can also work with monitoring tooling you already have in place.
See it in practice: Konsolute provides Great British Energy – Nuclear with security-cleared managed support from first line to third line.
Service boundaries
Clear coverage, security and responsibilities
Before onboarding we agree what is monitored, how alerts are handled, response responsibilities, escalation paths and who can authorise changes. This gives both teams clear operational ownership when an alert occurs.
Monitoring hours & alert response
Monitored services, alert priorities, response targets and hours of cover are agreed before go-live. Business-hours and 24/7 options are available.
Security monitoring & incidents
We can monitor selected Defender, Entra ID and Sentinel security signals and escalate potential or confirmed security incidents through your agreed security process. A dedicated SOC, managed detection and response, proactive threat hunting or forensic investigation is scoped separately.
Tooling & monitoring data
We primarily use Microsoft-native services including Azure Monitor, Log Analytics, Application Insights, Service Health and Network Watcher, supplemented by Konsolute Uata where appropriate. Monitoring data can remain within your Microsoft environment. Azure ingestion, retention and platform consumption charges remain part of your Azure subscription.
Optimisation changes & projects
Optimisation recommendations are reviewed with you before material changes are implemented. Routine monitoring and operational tuning can form part of the managed service. Re-architecture, migrations, major application changes and significant resilience projects are separately scoped where required.
FAQ
Monitoring and optimisation FAQs
Coverage, tooling, alert response, automation, security and pricing.
Konsolute can continuously monitor Azure infrastructure, Microsoft 365, applications, data services and selected security signals. Our engineers triage and investigate alerts, support remediation, analyse recurring issues and use monitoring data to identify opportunities to improve performance, resilience, capacity and cost.
Coverage can include Azure infrastructure and networking, Microsoft 365 Service Health, Entra ID, Microsoft Defender, Microsoft Sentinel integrations, Azure Monitor, Log Analytics, Application Insights, Azure Data Factory, Microsoft Fabric, Power BI, Azure Backup and other business-critical Microsoft services.
Yes. Business-hours and 24/7 monitoring options are available. The exact monitoring window, alert priorities, escalation process and response targets are defined in the agreed managed service.
We primarily use Microsoft-native capabilities including Azure Monitor, Log Analytics, Application Insights, Azure Service Health, Resource Health, Network Watcher, Azure Advisor and Microsoft Defender. Konsolute Uata can provide additional proactive visibility across your Microsoft ecosystem. Existing monitoring tooling can also be reviewed during discovery.
Monitoring tells us when known conditions or thresholds are reached. Observability goes further by correlating metrics, logs, traces, dependencies and application behaviour to help engineers understand why a service is behaving differently. Our managed service can use both approaches depending on the application and platform.
We establish normal operating behaviour, then configure alerts around the health of critical services rather than enabling every possible default rule. Thresholds, duplicate alerts, suppression rules and escalation routes are reviewed continuously so engineers and customers receive alerts that are meaningful and actionable.
An engineer assesses the alert, determines potential business impact and investigates the underlying telemetry. Depending on the agreed service scope, we can resolve the issue, trigger approved remediation, escalate it to a specialist or coordinate with your team or Microsoft. Recurring alerts are reviewed to identify and address their root cause.
For known and repeatable scenarios, approved automation, workflows or runbooks can be used to perform predefined remediation actions. More complex or higher-risk incidents remain subject to engineering investigation and your agreed change and approval processes.
We analyse monitoring and operational data alongside services such as Azure Advisor and Well-Architected guidance to identify performance bottlenecks, resilience risks, capacity requirements, monitoring gaps and unnecessary spend. Recommendations are prioritised through regular service reviews, with routine operational tuning included where agreed.
No. The service can monitor and triage selected Defender, identity and Microsoft Sentinel security signals and route potential incidents through your agreed security process. Dedicated threat hunting, managed detection and response, forensic investigation and full SOC services are separately scoped.
Yes. Konsolute supports public sector and regulated organisations, including environments where controlled access and security-cleared personnel are required. Monitoring access is designed around least privilege and agreed governance requirements, with engineers holding SC (Security Check) and DV (Developed Vetting) clearance where required.
Yes. The service can be fully managed or co-managed. Konsolute can provide specialist monitoring, out-of-hours coverage, escalation support, alert tuning and optimisation while your internal team retains responsibility for other operational activities. Ownership and escalation routes are documented during onboarding.
Pricing depends on the platforms and services in scope, the scale and complexity of the environment, monitoring hours, response requirements and the level of engineering responsibility Konsolute assumes. Microsoft platform charges such as Log Analytics ingestion and retention remain within your Azure subscription unless otherwise agreed.
Strengthen your resilience
Need a managed monitoring partner you can rely on?
Tell us about your Microsoft environment, your critical services and the operational challenges you want to solve. We'll help define the right monitoring, response and optimisation scope for your organisation.